More Breadth for Cortex with DomainTools IP Risk Feeds

Essential Context from DomainTools In Your Cortex Environment
Cortex by Palo Alto gives teams a unified way to quickly view, identify, and respond to relevant indicators. The broader the data Cortex can reach and the richer that context, the sooner a threat can be assessed, investigated, and stopped.
The DomainTools App for Cortex already gives users in-depth DNS indicators and domain risk. Today, we’re excited to release FeedDomainTools Pack v1.2, which brings our IP Risk and IP Hotlist feeds into Cortex. These additions, paired with the Model Context Protocol (MCP) capabilities we’ve released since the last Cortex update, widens the reach of information users can access.
The DomainTools IP Risk Feed delivers comprehensive risk intelligence for all IPv4 addresses known to be hosting domains, while the DomainTools IP Hotlist Feed focuses on the highest-risk hosting IP addresses. For more information check out our blog on the real-time delivery of both feeds. Security teams can now:
- Quickly Investigate the direction and indication of IP-based risk where domain hosting is that IP’s purpose or primary use
- Create ad-hoc, accurate blocklists for low-hanging fruit IP based risks, tailored to your risk profile
- Access our comprehensive datasets directly within your existing Cortex workflows
- Get hosting details, connected infrastructure, and full domain depth all by starting with a feed of IPs. Then the Risk Scores, registration details, history, certificate data, and passive DNS are all returned in one response by our MCP. No context switching or manual pivots required.
These capabilities are delivered by the two commands, domaintools-ip-hotlist-get and domaintools-ip-risk-get, with IP/DBotScore context outputs and war-room risk + hotlist rendering. By adding these commands, you can get ad-hoc war room enrichment as well as trigger playbook action based on the presence of hot or just plain risky IP addresses in your corpus of indicators, derived from DomainTools Real-Time IP Hotlist and Risk Feed Products.
Native Orchestration with DomainTools and Cortex
Because Cortex seamlessly connects integrated data across its entire framework, incident responders working out of Cortex XSOAR have access to all the context and data that CTI analysts working out of Cortex XSIAM have by default. This connected ecosystem makes Cortex the ideal environment to embed the DomainTools MCP Server.
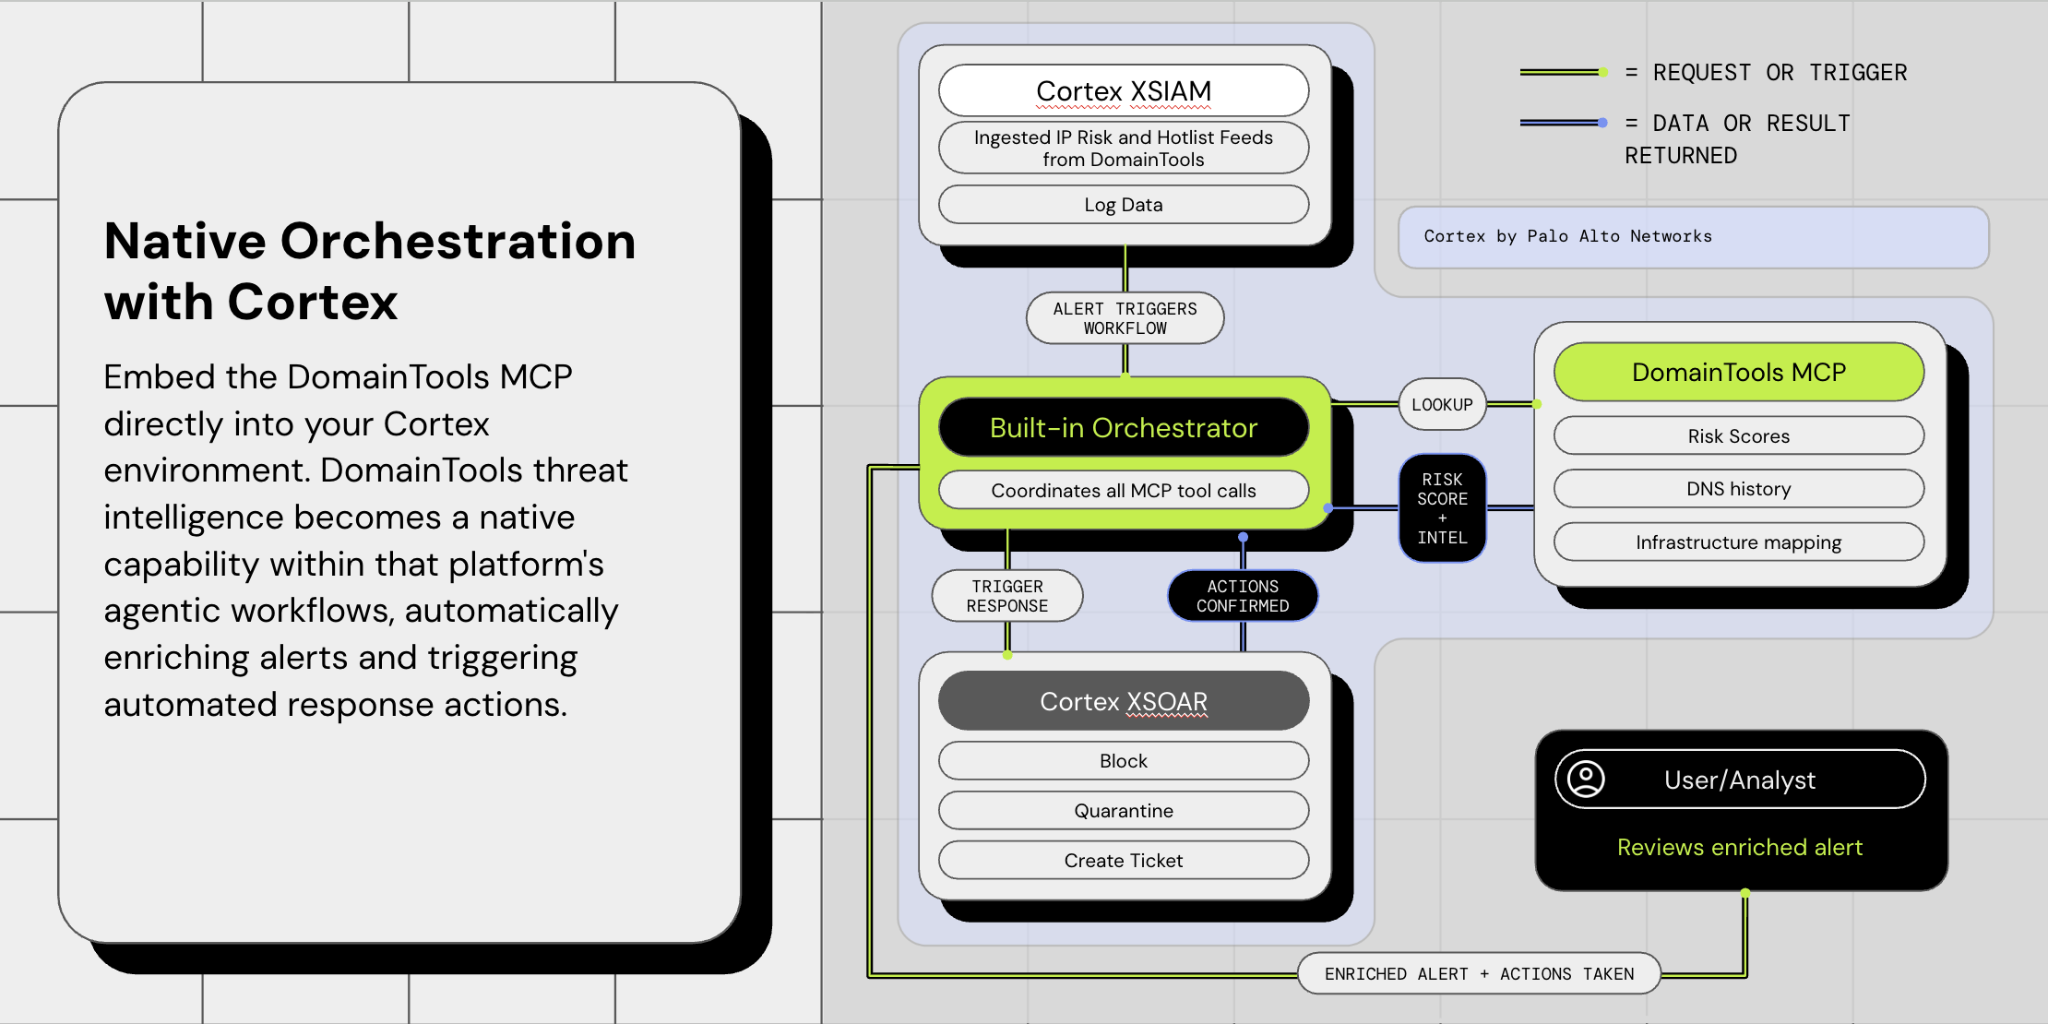
The diagram below visualizes how DomainTools MCP can be deployed within Cortex if you have Cortex AgentiX or any other LLM embedded in your Cortex environment acting as a built-in orchestrator. This orchestrator can be a part of Cortex XSIAM or Cortex XSOAR, and with how the ecosystem works together it’s easy for it to be a part of both. This orchestrator would be talking to its own native data source but can also call out to the DomainTools MCP Server to access our core domain intelligence datasets and retrieve actionable insights through conversation.
How it Works
Get started today by downloading the DomainTools Indicator Feeds for Cortex.